
Digital technology has transformed how people communicate, work, shop, learn, and manage their finances. From online banking and cloud storage to artificial intelligence and smart home devices, digital services have become an essential part of everyday life. However, this growing dependence on connected systems has also created new opportunities for cybercriminals. Stolen passwords, fraudulent messages, malicious software, and data breaches can affect individuals, businesses, and public institutions. Protecting digital information is no longer just a technical responsibility; it is an important part of maintaining privacy, financial security, and trust in the modern world.
Cyber security refers to the practices, technologies, and policies used to protect computers, networks, applications, and information from unauthorized access, damage, theft, and disruption. As digital threats become more sophisticated, traditional precautions alone may not be sufficient. Criminals increasingly exploit human behavior, weak authentication, outdated software, and poorly protected systems to achieve their goals. Understanding these risks helps individuals and organizations make informed decisions about their digital safety. By combining reliable technology with responsible online habits, people can reduce their exposure to common attacks and build a stronger foundation for using digital services confidently.
Understanding the Importance of Cyber Security
The importance of digital protection extends far beyond preventing computer viruses. Personal devices contain private photographs, financial records, professional documents, saved passwords, and conversations that should remain confidential. If an attacker gains access to an account, the consequences may include identity theft, financial loss, impersonation, or exposure of sensitive information. For businesses, a single security incident can interrupt operations, damage customer relationships, and create expensive recovery requirements. Organizations that depend on digital platforms must therefore consider information protection an essential part of their overall business strategy.
Effective cyber security also supports the reliability and availability of digital services. Imagine a hospital whose computer systems become unavailable during an emergency or a small company that loses access to its customer database after a ransomware attack. Such incidents demonstrate that digital risks can have consequences beyond the immediate loss of data. Prevention, early detection, and recovery planning help reduce disruption and protect the people who depend on these systems. As more essential services move online, maintaining secure and dependable technology becomes increasingly important for individuals, communities, and economies.
Common Cyber Threats in the Modern Digital Environment
Cyber threats continue to evolve as attackers adopt new tools and refine familiar techniques. Phishing remains a widespread problem because it targets human judgment rather than relying exclusively on technical weaknesses. A fraudulent email or text message may appear to come from a bank, delivery company, employer, or government department. The message might create urgency by claiming that an account will be suspended or a payment has failed. When a recipient clicks a deceptive link, shares a verification code, or opens a harmful attachment, the attacker may gain access to confidential information.
Malware and ransomware present additional challenges. Malware is software designed to perform harmful or unauthorized activities, such as stealing information, monitoring behavior, or disrupting devices. Ransomware can encrypt files or prevent access to important systems while demanding payment for restoration. Another significant threat involves credential theft, where criminals obtain usernames and passwords through deception, data breaches, or automated guessing. Attackers may also exploit software vulnerabilities that remain unpatched. These threats are different in their methods, but they often share the same objective: gaining unauthorized access, stealing valuable information, or interfering with digital operations.
How Cyber Security Protects Personal Information
Personal information has considerable value because it can be used for identity fraud, targeted scams, account takeovers, and unauthorized financial transactions. Protecting this information begins with understanding what is being shared online and which services genuinely require it. Social media profiles, online shopping accounts, mobile applications, and digital subscriptions may collect different types of personal data. Sharing unnecessary details can increase exposure, especially when information from several platforms can be combined to create a more complete picture of someone’s identity.
Strong account protection reduces the chances that stolen information will lead to further damage. Unique passwords help prevent a compromised account from exposing several other accounts at once. Multifactor authentication adds another verification step, making unauthorized access more difficult even when a password has been stolen. Privacy settings, careful app permissions, and regular account reviews also contribute to safer digital habits. These measures may appear simple, but consistently applying them can significantly improve personal protection and limit the potential consequences of an online attack.
Essential Practices for Strong Digital Protection
Good security depends on a combination of technology, awareness, and consistent maintenance. People do not need to become technical specialists to make meaningful improvements. They can begin by updating devices, securing important accounts, and learning to recognize suspicious messages. Businesses can build on these habits by introducing clear security policies, controlling employee access, and maintaining reliable backup systems. The most effective approach focuses on reducing avoidable risks while preparing for the possibility that an incident could still occur.
Several practical measures can help individuals and small organizations strengthen their everyday protection:
-
Use long, unique passwords for different accounts and store them in a reputable password manager.
-
Enable multifactor authentication, especially for email, banking, cloud storage, and administrative accounts.
-
Install operating system, browser, and application updates promptly.
-
Avoid opening unexpected attachments or sharing passwords and verification codes.
-
Maintain separate, reliable backups of important files and test whether they can be restored.
These actions are most effective when practiced consistently rather than only after a security warning appears. For example, keeping an independent backup can make recovering from ransomware or accidental deletion much easier. Similarly, verifying a suspicious request through a known telephone number or trusted communication channel can prevent an attacker from impersonating a colleague or service provider.
The Role of Artificial Intelligence in Cyber Security
Artificial intelligence is changing how security teams identify suspicious behavior, investigate incidents, and respond to emerging threats. Machine learning systems can analyze large volumes of network activity and highlight patterns that may indicate unauthorized access. Automated monitoring can help identify unusual login locations, unexpected data transfers, or repeated attempts to access restricted systems. By reducing the time needed to examine routine alerts, these tools can help security professionals focus on incidents that require deeper investigation.
However, artificial intelligence also creates new challenges. Criminals can use generative tools to produce convincing phishing messages, imitate communication styles, and develop more personalized scams. Deepfake audio and video may be used to impersonate executives, colleagues, or family members. A realistic voice message requesting an urgent payment should therefore not be accepted as proof of identity. Organizations can reduce these risks by establishing verification procedures, restricting sensitive transactions, and training employees to question unusual requests. AI-based security tools are valuable, but human oversight remains necessary because automated systems can make mistakes and attackers continually adapt.
Cyber Security for Businesses and Organizations
Businesses face a broad range of digital risks because they manage customer information, payment systems, internal communications, intellectual property, and operational data. Small companies may assume that criminals primarily target large corporations, but attackers often look for easier entry points, including poorly secured websites, outdated applications, and weak employee accounts. A successful incident can interrupt sales, delay services, expose confidential records, and damage a company’s reputation. Security planning should therefore be proportionate to the sensitivity of the information and the potential impact of a disruption.
A well-designed organizational security program begins with identifying important assets and understanding the risks associated with them. Access should be limited according to job responsibilities, and administrative privileges should be granted only when necessary. Employees need regular training on phishing, password management, information handling, and incident reporting. Businesses should also establish procedures for responding to suspicious activity, notifying appropriate stakeholders, restoring systems, and reviewing what went wrong. In this environment, cyber security becomes a shared responsibility involving leadership, technical teams, employees, and external service providers.
Understanding Different Security Measures
Different protective measures address different parts of the digital environment. Firewalls help control network traffic according to defined rules, while endpoint protection tools monitor computers and other devices for malicious activity. Encryption helps keep information unreadable to unauthorized parties, provided that the relevant cryptographic keys remain protected. Backup systems support recovery, while access controls determine who can view or change particular resources. No single technology provides complete protection, which is why organizations often combine several safeguards.
The following table explains the main purpose of common security measures and where they are useful.
| Security measure | Primary purpose | Common application |
|---|---|---|
| Firewall | Controls network connections | Home and business networks |
| Multifactor authentication | Adds an identity verification step | Email and financial accounts |
| Encryption | Protects information from unauthorized reading | Data storage and communication |
| Endpoint protection | Detects and blocks harmful activity | Laptops and desktop computers |
| Data backups | Supports recovery after data loss | Personal files and business records |
Choosing suitable measures requires understanding the risks involved. A freelancer handling client documents may prioritize encrypted storage, secure email accounts, and regular backups. A company operating an online store may also need payment security, website monitoring, access restrictions, and a documented incident response plan. The goal is to build multiple layers of defense so that the failure of one safeguard does not automatically expose the entire system.
Cloud Computing, Remote Work, and Connected Devices
Cloud computing has made it easier to store files, run applications, collaborate with colleagues, and access information from different locations. Remote work has increased this flexibility, but it has also expanded the number of devices and connections that organizations must protect. Employees may connect through home routers, personal laptops, public networks, or mobile devices. If these systems are poorly configured, attackers may find opportunities to access business resources. Organizations can reduce these risks by requiring secure authentication, controlling device access, and applying appropriate protections to sensitive information.
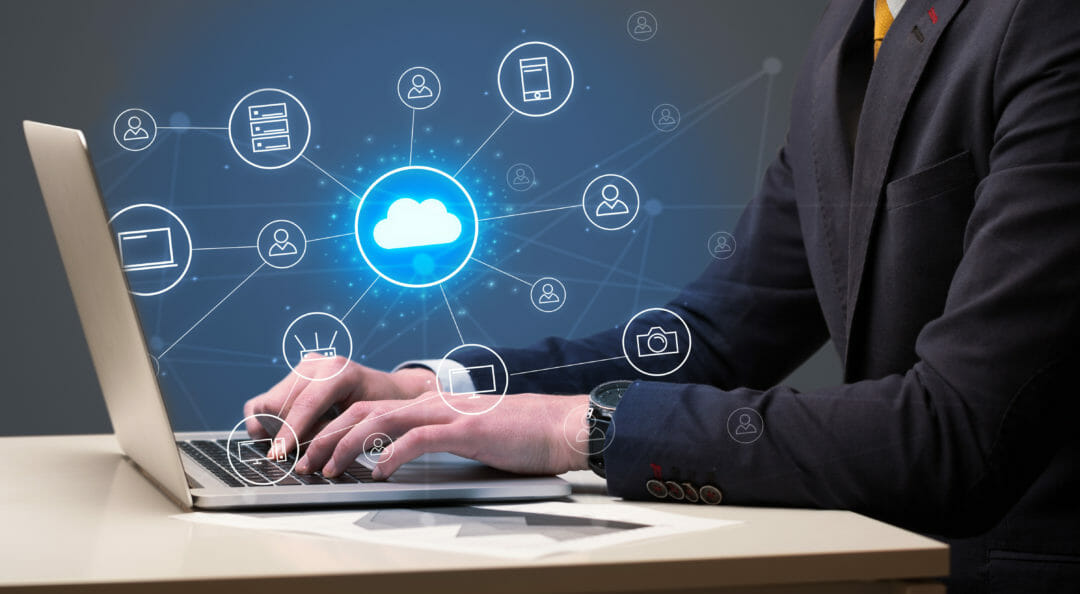
Connected devices introduce similar concerns. Smart televisions, cameras, home assistants, industrial sensors, and other Internet of Things products may collect data or communicate with external services. Some devices receive infrequent security updates or retain default passwords that are easy to guess. Users should change default credentials, install available firmware updates, disable unnecessary features, and place less-trusted devices on separate networks when practical. Businesses should also review the security practices of their cloud providers and technology partners. Responsibility for protection may be shared, but it should never be assumed that a service provider automatically manages every security setting.
Developing a Security-Aware Digital Culture
Technology alone cannot eliminate digital risk because many attacks depend on decisions made by real people. An employee may approve an unexpected login request, a customer may disclose a verification code, or a manager may authorize a fraudulent payment after receiving a convincing message. These incidents demonstrate why awareness must be part of everyday digital behavior. People should feel comfortable reporting suspicious activity without fearing embarrassment or punishment for asking questions.
Organizations can support this culture through practical training, clear reporting channels, and realistic exercises. Instead of relying only on annual presentations, businesses can provide short learning sessions that explain current scams and demonstrate how to verify unusual requests. Leadership should model careful behavior and make security expectations understandable. Individuals can adopt the same mindset by pausing before acting on urgent messages, checking the identity of unexpected callers, and reviewing account alerts. Responsible habits create an additional layer of defense that supports technical safeguards.
The Future of Digital Security
The future of digital protection will be shaped by developments in artificial intelligence, cloud infrastructure, identity management, and connected technology. Passwordless authentication methods, including passkeys, can reduce reliance on traditional passwords when properly implemented. Zero-trust security models emphasize verifying users and devices before granting access rather than automatically trusting everything inside a network. Automation may also help organizations detect threats more quickly and respond to certain incidents with less manual effort.
At the same time, emerging technologies will introduce unfamiliar vulnerabilities. Organizations will need to assess how AI systems handle sensitive information, who can access automated tools, and whether third-party services create additional exposure. Quantum computing may eventually affect some widely used cryptographic methods, making long-term preparation important for systems that must protect information for many years. Future readiness will require regular risk assessments, updated policies, employee education, and investment in appropriate technology. Rather than relying on a single new solution, successful protection will depend on the ability to adapt as the digital environment changes.
Conclusion
Protecting digital information requires more than installing security software or choosing a complicated password. It involves understanding common threats, recognizing suspicious behavior, limiting unnecessary access, updating technology, and preparing for unexpected incidents. Individuals can improve their safety by protecting accounts and personal information, while organizations can strengthen their defenses through training, monitoring, access controls, and tested recovery plans. Each measure addresses a different weakness, and their combined effect creates a more resilient digital environment.
As technology continues to influence communication, business, education, and personal finance, cyber security will remain a fundamental part of responsible digital participation. New threats will emerge, but informed decisions and consistent protective practices can reduce their impact. By treating security as an ongoing process rather than a one-time task, individuals and organizations can protect valuable information, maintain trust, and use modern technology with greater confidence.